Clarity. Responsibility. Intelligence.

SentiQ
From risk you can't see to evidence you can show

Most companies have security tools. Few can show they work. When an auditor, a customer or your board asks for proof, a folder of policies is not an answer.

SentiQ helps you build proven security: measures that run day to day and leave evidence you can show.

Senior, independent advisory with hands-on depth across AI, cybersecurity and cloud.

No fluff. No vendor lock-in.

We work primarily with small and mid-sized companies across Europe that need to get AI, security and cloud right. Especially now, with the first NIS2 audits landing in 2027 and AI Act deadlines approaching.

CISSP CCSP ISO 27001 Lead Auditor ISO 42001 Lead Auditor Certified Cybersecurity Manager (SK)

Independent multi-discipline advisory · 30 years in IT · Clients in finance, utilities, professional services and more

Our Services

What we do

Assess → Advise → Design → Build → Harden → Run.
One senior architect leads the whole cycle. Your team or trusted partners build and run it, to our design and under our review. It ends in proof.

AI Advisory & Governance

From AI Act compliance to production-ready governance. We make AI adoption safe, structured and defensible.

Includes:

  • AI governance frameworks & strategy
  • AI policies, acceptable use & playbooks
  • Readiness assessments for Copilot & custom AI
  • AI supplier due diligence audits
  • Landing zone checklists (PoC, Prod)
  • AI workload hardening, CSPM, CWPP
  • AI Act, ISO 42001, NIST AI RMF

Typical engagement: assessment, framework design or ongoing advisory

Cybersecurity

Security architecture, risk management and compliance. Built around your real exposure, not generic checklists.

Includes:

  • Security architecture & SOC design
  • Compliance assessments & prioritized remediation
  • M365 & Azure security architecture (Entra ID, Conditional Access, Defender, Purview)
  • Copilot readiness & data exposure review
  • AI workload security & data protection
  • Incident response process design
  • NIS2, ISO 27001, NIST CSF

Typical engagement: assessment, architecture review or security roadmap

Cloud & IT

Our IT team keeps your Microsoft 365 and Azure running: setup, migration and everyday support. Security design comes from our cybersecurity practice.

Includes:

  • Microsoft 365 & Azure setup and management
  • Cloud migration, including email to Microsoft 365
  • IT support for your team
  • Copilot and AI tools setup
  • Licence & cost optimization

Typical engagement: project-based or ongoing support

What you get

From the business side

  • Assessment reports with heatmaps and findings
  • Board-ready roadmaps and project priorities
  • AI governance frameworks and playbooks
  • Compliance gap analysis with evidence and controls
  • Prioritized project list with effort and cost estimates

From the technology side

  • Security architecture and SOC designs
  • Technology recommendations, products and licences
  • Sentinel, Defender and Purview designs and baselines
  • A plan your team can execute without hand-holding
  • Security that holds up in an audit
Why SentiQ

Why choose SentiQ

Business needs and technology move fast, in different directions. We connect them so you can move forward with confidence.

Senior-led & Independent

You work directly with experienced practitioners. No junior handoffs, no layers

Secure & Responsible

Security, compliance and governance are built into the design and the process

Bridging Both Sides

Business goals and regulations translated into concrete technology decisions and controls

Actionable Results

Pragmatic outcomes, clear structure and real impact you can see and measure

About the Founder

The vision behind SentiQ
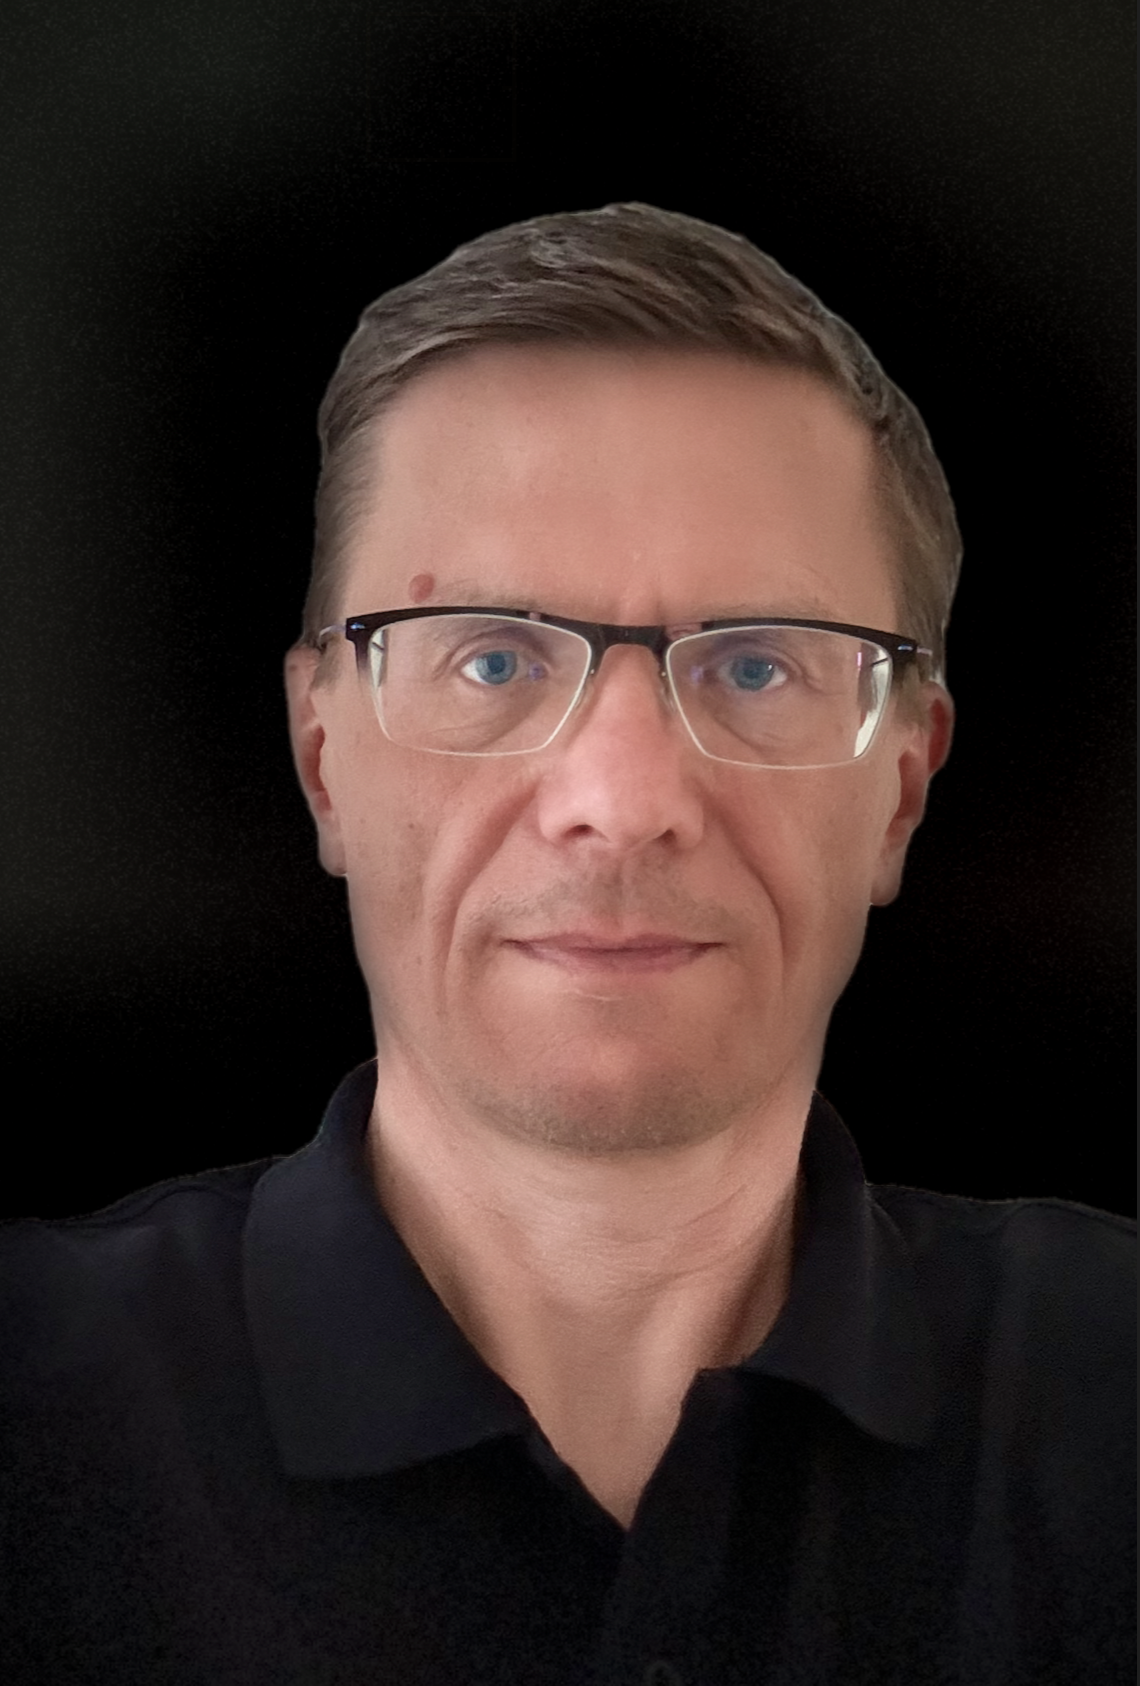
Jan Paulech, Founder of SentiQ

Jan Paulech

Security & AI Architect, Advisor
LinkedIn

Jan has three decades of experience on the vendor side of IT. Now he uses it to advise you independently. He spent 17 years at Microsoft in leadership roles across Central and Eastern Europe, most recently leading security sales and technical specialists across 20+ countries. His earlier career includes roles at Hewlett-Packard, Compaq and Digital Equipment Corporation.

Today he combines his Microsoft experience and cloud and governance expertise with CISSP, CCSP, Lead Auditor certifications for ISO 27001 and ISO 42001 and certification as a Cybersecurity Manager under Slovak law. His focus is on AI security, NIS2 readiness and helping organizations translate regulatory requirements into practical controls.

He founded SentiQ because he saw the same pattern everywhere: business leaders under pressure from regulations and governance on one side, and rapidly evolving technology on the other. No single team can stay on top of both. SentiQ was built to bridge that gap, turning business and compliance goals into practical technology decisions, specific products, configurations and controls. So that leaders, managers and owners can move forward confidently and sleep well.

The name SentiQ reflects what we believe in. Sense comes from people: judgment, experience and understanding. Intelligence comes from pairing that sense with smart technology. SentiQ is where the two meet. Making sense of complexity is what we do.

SentiQ is deliberately small. You get direct access, hands-on guidance and pragmatic outcomes.

Contact

Let's talk

Based in Bratislava, Slovakia. Working with clients across Europe.

Send us a message

A simple conversation to get started.

Message sent

Thank you. Your message has been delivered.

We typically respond within one business day.